Traditional Code Security Is Broken
Traditional SAST, DAST, and SCA tools generate thousands of false positives because they scan code in isolation, without understanding your application's architecture. Teams waste 60-80% of their time triaging findings that are not actually exploitable.
Without Architecture Context
- ✗ 3,000+ findings per scan, 80% are false positives
- ✗ No understanding of trust boundaries or data flows
- ✗ Internal-only services flagged as critical risks
- ✗ Dead code paths generate high-severity alerts
- ✗ Developers ignore security due to alert fatigue
With Aristiun
- Near-zero false positives, because the scanner knows your architecture
- Trust boundaries and data flows built into scanning
- Severity adjusted based on deployment architecture
- Only reachable code paths are flagged
- Developers trust and act on every finding
SAST + DAST + SCA, All Architecture-Aware
Complete application security testing with the context of your actual architecture. Click each layer to learn more.
SAST
Static Application Security Testing
Analyzes source code, bytecode, and binaries without executing the application. Identifies vulnerabilities at the earliest stage of development.
What It Catches
- SQL injection patterns
- Cross-site scripting (XSS)
- Buffer overflows
- Hardcoded secrets & credentials
- Insecure cryptographic usage
How Aristiun Improves It
Aristiun's architecture-aware SAST understands which code paths are reachable from external inputs based on your actual architecture diagram. It eliminates findings in dead code, internal-only services, and sandboxed components.
Architecture-Aware Scanning
Aristiun scans understand your architecture diagram, know which components talk to what, and understand trust boundaries. This context is what eliminates false positives.
Trust Boundary Awareness
Scans understand which components sit behind firewalls, API gateways, or service meshes, and adjust severity accordingly.
Data Flow Tracing
Traces how user input flows through your architecture to determine if a vulnerable code path is actually reachable from an attack surface.
Component Interaction Mapping
Maps which services talk to which databases, queues, and third-party APIs, so findings reflect real risk.
False Positive Elimination
By understanding architecture context, Aristiun eliminates the 60-80% of findings that traditional tools flag but are not exploitable.
Context Eliminates False Positives
✗ Traditional Scanner — CRITICAL
SQL Injection in UserRepository.findByEmail()
Flagged as critical in ALL environments regardless of context
✓ Aristiun — SUPPRESSED (Not Exploitable)
SQL Injection in UserRepository.findByEmail()
→ Component: internal-admin-service
→ Trust Boundary: behind VPN + WAF + API Gateway
→ Data Flow: no external input reaches this path
→ Verdict: not exploitable in current architecture
Secure Your Software Supply Chain
SBOM generation, dependency scanning, license compliance, and vulnerability tracking for transitive dependencies. Integrated with the tools you already use.
SBOM Generation
Automatic Software Bill of Materials in CycloneDX and SPDX formats for every build.
Dependency Scanning
Deep scanning of direct and transitive dependencies across npm, PyPI, Maven, NuGet, Go modules, and more.
License Compliance
Automatic detection of GPL, AGPL, and other copyleft licenses with policy enforcement and approval workflows.
Transitive Vulnerability Tracking
Traces CVEs through the full dependency tree to find hidden risks in nested packages.
Malicious Package Detection
AI-powered detection of typosquatting, dependency confusion, and known malicious packages before they enter your supply chain.
Continuous Monitoring
Real-time alerts when new CVEs are published for any dependency in your tracked projects.
Security in Every Pipeline
Per-commit scanning, PR blocking on critical vulnerabilities, and native integrations with GitHub, GitLab, and Azure DevOps.
Per-Commit Scanning
Every commit triggers an architecture-aware scan. Results appear inline in your pull request within minutes.
PR Blocking on Critical Vulns
Configure policies to block merges when critical or high-severity vulnerabilities are detected.
GitHub / GitLab / Azure DevOps
Native integrations with all major Git platforms. One-click setup with pre-built workflow templates.
Pipeline Security Gates
Insert Aristiun as a gate in your CI/CD pipeline. Pass or fail builds based on customizable security thresholds.
Works with Your Existing Tools
Aristiun aggregates findings from all your security scanners, deduplicates them, and applies architecture context. One platform for all your scan results.
Security by the Numbers
Real results from architecture-aware code security scanning.
Frequently Asked Questions
Everything you need to know about architecture-aware code security, SAST/DAST/SCA, and supply chain protection.
Part of the Unified Security Workbench
Code security doesn't exist in isolation. Aristiun's workbench connects code vulnerabilities to your architecture's digital twin, validating every finding against actual trust boundaries, data flows, and deployment context. Shadow AI agents writing code? Discovered and governed. Compliance impact? Auto-mapped to 340+ frameworks.
Powered by Ayurak AI
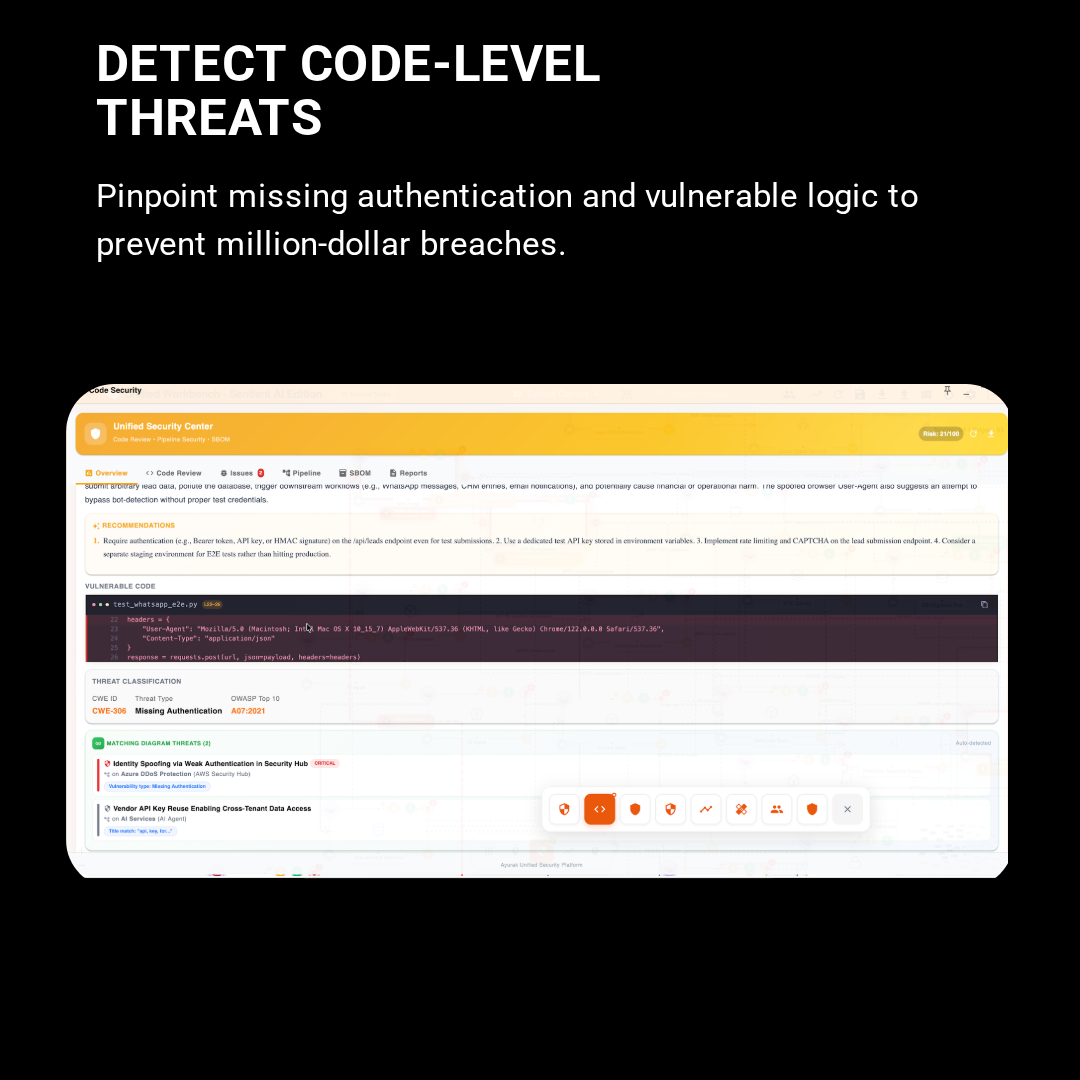
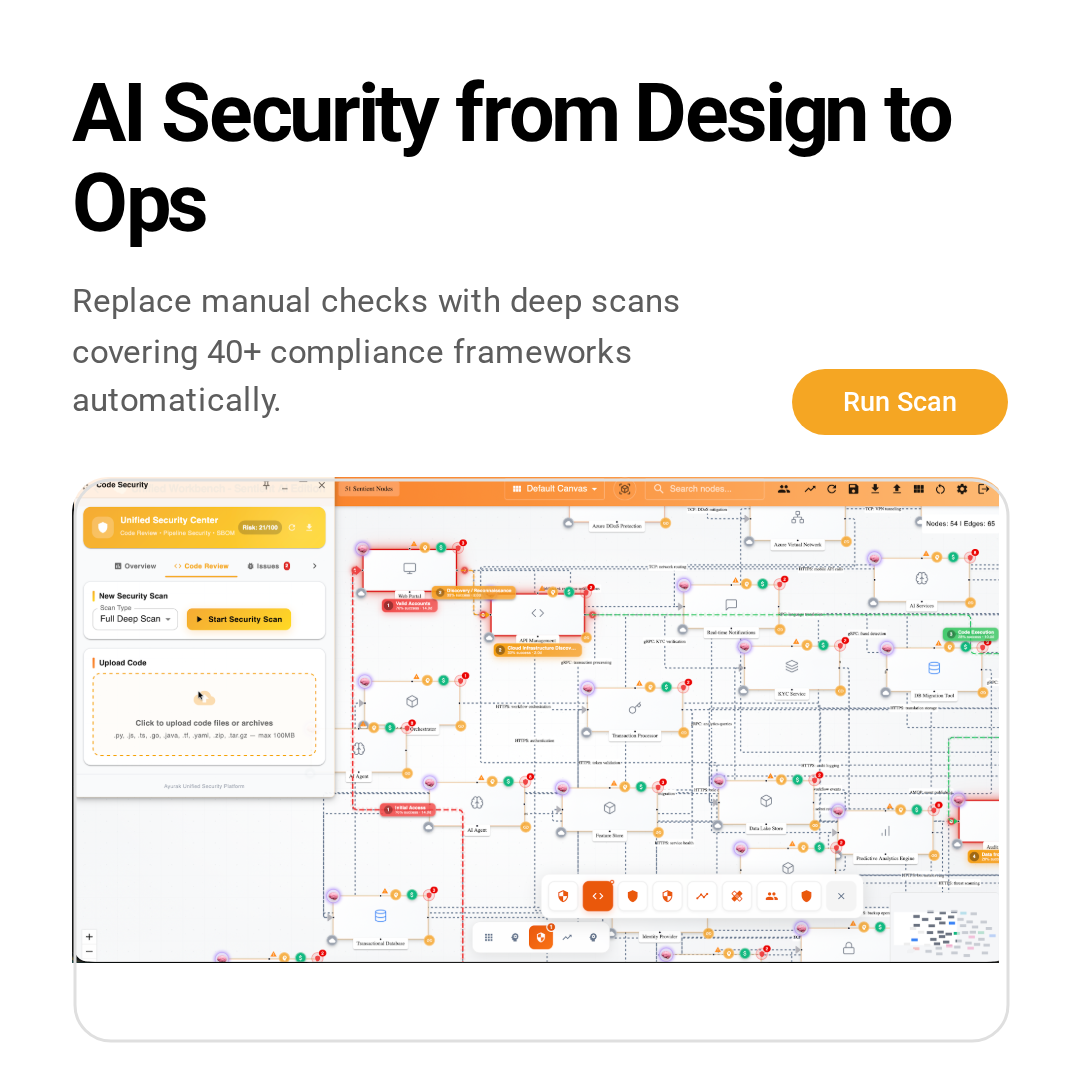
Code Security in Action
Aristiun maps code-level vulnerabilities back to the architecture context where they actually matter.
Explore Related Solutions
Automated Threat Modeling
AI-powered STRIDE, PASTA, and LINDDUN analysis for your architecture
Learn moreAI Security
Shadow AI discovery and LLM governance for enterprise AI stacks
Learn moreCompliance Automation
Map controls across 340+ frameworks with continuous evidence collection
Learn moreThreat Modeling as Code
Integrate threat analysis into your CI/CD pipeline
Learn more